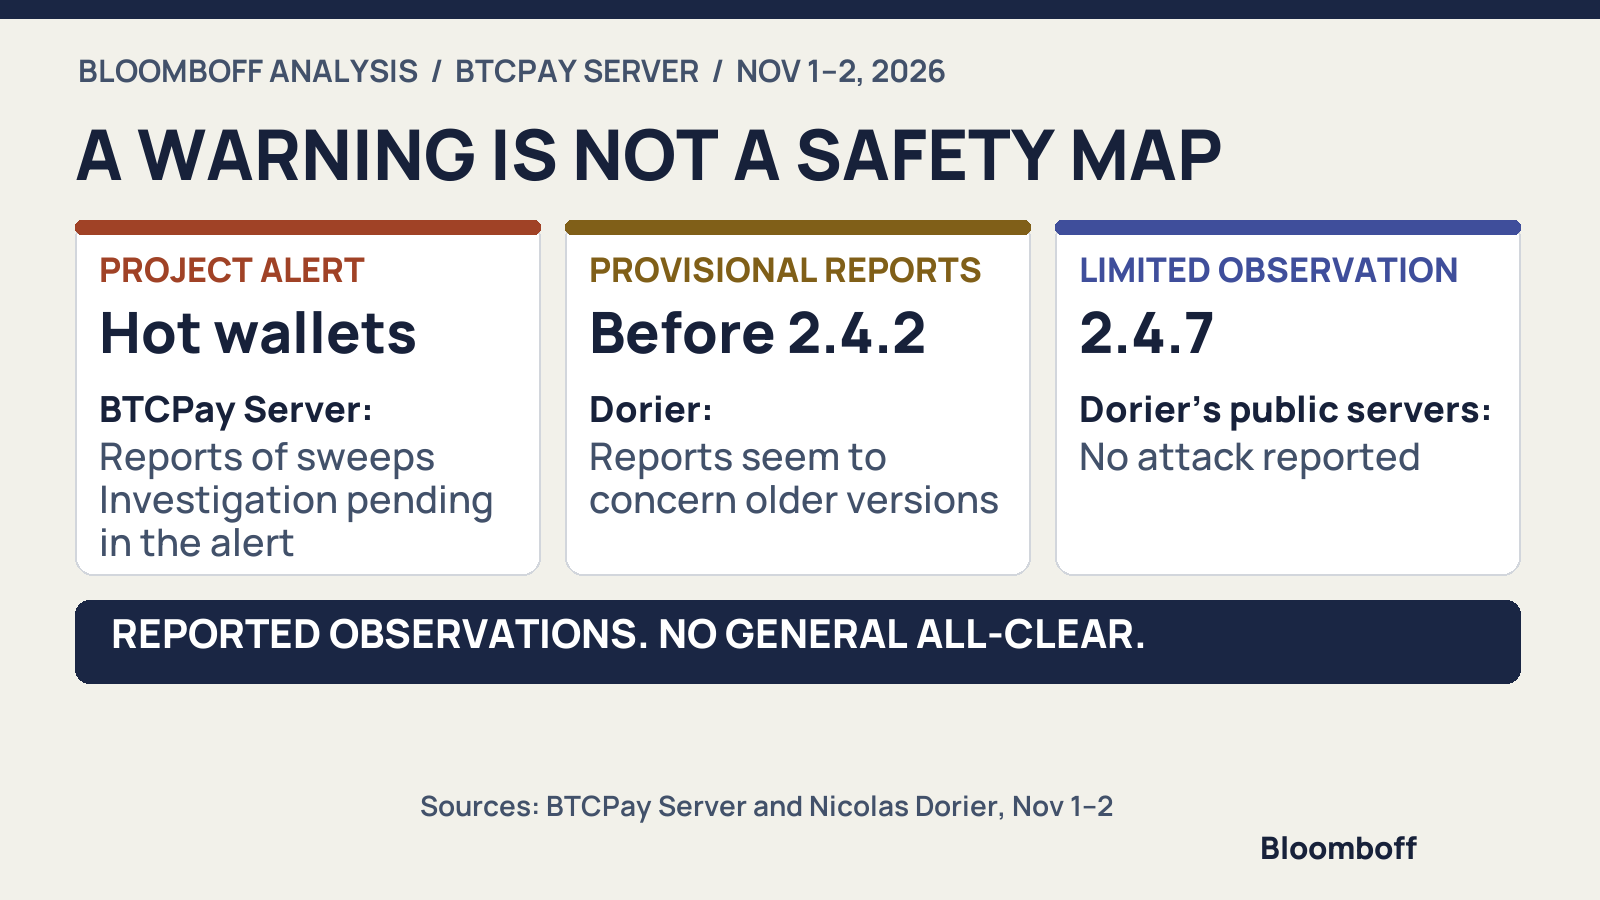
- BTCPay Server requested a shutdown while investigating reported hot-wallet sweeps.
- Dorier said reports seemed to concern versions before 2.4.2.
- A later reply promised more detail in a blog post.
BTCPay Server asked instance operators to shut down pending investigation after receiving reports of unauthorized hot-wallet sweeps on Nov. 1.1
Nicolas Dorier later said his public servers, running 2.4.7, had not been attacked. Reports seemed to concern versions before 2.4.2; an attacker had logged in as administrator, but how remained unknown.2
In a subsequent reply, Dorier said traces pointed to vulnerabilities predating 2.4.2 and promised more detail in a blog post.3 These are attributed accounts, not Bloomboff's independent forensic findings.
Bloomboff's take
Version numbers are not force fields. His report of unaffected servers is not a safety certificate for every installation. Keep the broad warning separate from the provisional scope. Reading that scope as a universal all-clear is expensive bullshit.